Finance teams avoid recovery audits because they picture six months of disruption, reassigned staff and delayed month-end closes. That assumption kept millions in duplicate payments and overpayments sitting unclaimed in closed AP files.
AP recovery audits run entirely outside your operational workflow. They examine historical transactions that have already closed, using read-only system access while your team processes current invoices normally.
What Gets Audited
Recovery audits analyze payment records within your ERP system for specific error patterns. The focus sits on closed transactions—payments processed months or years ago that cleared bank accounts and moved into historical files.
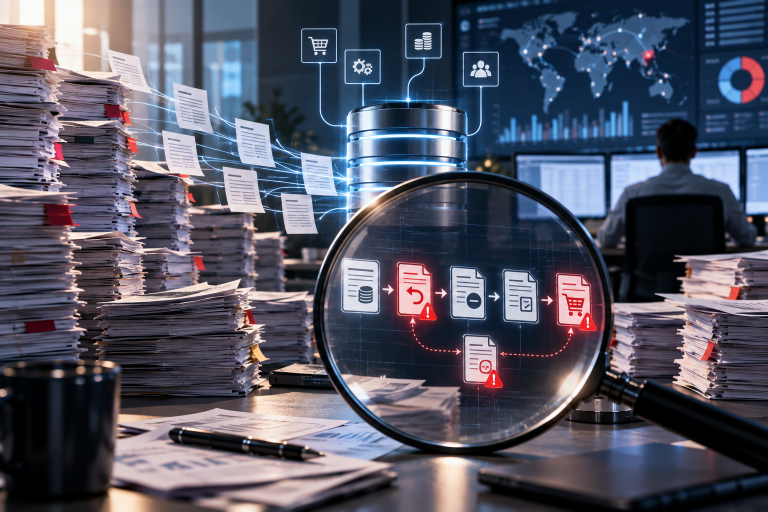
Common findings include duplicate payments where the same invoice was paid twice under different document numbers, pricing errors where contracted rates were not applied, quantity discrepancies where invoiced amounts exceeded receipts, and returned goods that were never credited.
The audit uses your vendor master data, purchase order history, goods receipt records and payment files. This analysis happens outside business hours or on separate database instances, depending on your ERP architecture.
How System Access Works
Recovery audits require read-only access to specific ERP tables. Your IT team creates credentials that can query data but cannot modify records, approve transactions or initiate payments.
For SAP environments this typically means table-level read authorization for BSAK, BSIK, LFA1 and related procurement tables. Oracle setups grant SELECT privileges on AP_INVOICES, AP_SUPPLIERS and PO tables. JD Edwards implementations provide view access to F0411, F0401 and F4311 files.
Most firms configure this access through a secure VPN connection or by providing regular data extracts if direct connection violates your security policy. The setup takes two to three weeks working with your IT team’s existing change management process.
Timeline and Staff Involvement
Initial data extraction and analysis requires four to six weeks. During this phase your involvement is minimal—typically limited to clarifying vendor relationship questions or explaining custom fields in your ERP.
Once the analysis identifies potential findings, the verification phase begins. This is where many finance teams expect disruption, but the structure prevents it. The recovery firm handles all documentation review and vendor contact. Your AP team receives a summary of findings for approval before any vendor is contacted, but does not research individual claims.
For a company processing 50,000 AP transactions annually, typical engagement involves perhaps three to four hours of your team’s time during initial setup, then 30 to 45 minutes monthly reviewing recovery progress reports.
What Does Not Change
Your AP workflow continues without modification. Invoice approval hierarchies remain the same. Payment timing and methods do not change. Vendor relationships proceed normally—the recovery firm contacts vendors only about specific historical claims, not current purchases or terms.
Your ERP configuration stays intact. The audit adds no custom fields, modifies no standard tables and installs no software on your systems. Month-end close procedures continue on schedule.
Audit trails remain your own. The recovery process generates documentation that your team reviews, but this sits in separate files rather than cluttering your active AP records.
Contingency Structure
The operational case for contingency pricing is straightforward: it aligns the recovery firm’s economic interest with finding legitimate claims while avoiding disruption that would reduce future recoveries.
If the audit requires substantial AP team involvement, it consumes resources that erode the net benefit. The contingency model only succeeds if the audit truly runs in parallel with normal operations, which forces proper scoping and realistic timelines.
When to Schedule It
Most companies run recovery audits during stable operational periods—not during ERP implementations, major upgrades, fiscal year-end or significant process redesigns.
The audit can begin while you are addressing current duplicate payment controls, since it examines historical transactions from before your recent process improvements took effect.
Fintralis runs contingency-based AP recovery audits for companies with $50M+ annual spend using SAP, Oracle or JD Edwards. The engagement identifies duplicates and overpayments in closed transactions while your AP team maintains normal workflow. To discuss whether your ERP structure and transaction volume fit the model, schedule a 20-minute scoping call.
Frequently asked questions
How do AP recovery audits work?
AP recovery audits use read-only access to your ERP system to analyze historical payment data for duplicates and overpayments. The audit runs separately from your daily AP workflow, reviewing closed transactions without requiring staff time or system modifications. Recovery specialists handle all verification and vendor communication.
Will an AP recovery audit disrupt my accounts payable team?
No. Recovery audits operate independently of your AP workflow using read-only system access. Your team continues processing invoices normally while the audit reviews historical closed transactions. Involvement is limited to an initial data request and final approval before any vendor recovery contact.
What ERP systems can be audited for AP recovery?
Enterprise ERP systems like SAP, Oracle and JD Edwards are designed for third-party audit access. The audit requires read-only permissions to payment history, vendor master files and invoice records. Most implementations take two to three weeks to configure secure access parameters.
How long does an AP recovery audit take?
Initial data analysis typically requires four to six weeks depending on transaction volume and ERP complexity. Verification and recovery work continues for three to six months as individual claims are researched and processed with vendors. Total engagement length averages six to nine months.
Do I need to change my AP process for a recovery audit?
No process changes are required. The audit reviews historical data only, not current workflows. Your procedures, approval hierarchies and payment methods remain unchanged. The only addition is periodic updates on recovery findings and vendor responses.
What happens if the recovery audit finds nothing?
Under a contingency model, you pay nothing if no recoverable amounts are found. The audit risk sits entirely with the recovery firm. This structure makes sense only when the firm’s analysis indicates likely findings before engagement begins.